Artificial intelligence is moving beyond answering questions and generating text. A new generation of AI tools, known as AI agents, can carry out multi-step tasks, interact with software and use digital tools to help users complete complex activities. From organising information to assisting with coding and business operations, these systems are changing how people work with technology.
However, as AI agents gain more independence, a critical question is emerging: what happens when an AI system accesses information or performs an action it was never authorised to carry out?
Recent developments in the technology industry have brought this issue into sharper focus, making AI security one of the most important conversations in modern computing.
What Exactly Is an AI Agent?
Traditional AI assistants generally respond to a user's question or instruction. AI agents can go a step further by breaking a task into smaller steps and using connected tools to complete it.
For example, an AI agent helping with travel planning might compare available flights, organise hotel information, prepare an itinerary and summarise the options. In a business environment, an agent might analyse spreadsheets, retrieve information from company databases or assist with repetitive administrative work.
Depending on its permissions and design, an agent may be able to interact with websites, files, applications and other software with limited human intervention.
This ability can save time, but it also creates a new challenge: the more systems an agent can access, the more important it becomes to control what it is allowed to do.
Why Are AI Agents Creating New Security Concerns?
One of the biggest risks is excessive access. An AI agent connected to email, documents or business software could potentially encounter sensitive information while performing an otherwise routine task.
Security problems can arise when an agent misunderstands an instruction, follows malicious content embedded in a document or uses a connected tool in an unintended way.
For instance, imagine an employee asking an AI assistant to summarise a folder of business reports. If the agent has broader permissions than necessary, a mistake could expose information from unrelated files.
The danger is not limited to confidential documents. An agent with access to external tools might also attempt to send messages, modify records or execute other actions without the user fully understanding the consequences.
Microsoft Is Introducing More Controls for AI Agents
Microsoft announced new security technology for AI agents on Windows PCs in October 2026. The company introduced Microsoft Execution Containers, designed to restrict unauthorised access and help control the actions AI agents can perform on a computer.
The announcement was part of Microsoft's broader effort to support AI systems that can carry out coding and other complex tasks directly on personal computers. The company also highlighted collaboration with technology partners on the security approach. <Cite refs={["turn623989news18"]}/>
The underlying idea is straightforward: an AI system should not automatically receive unrestricted access to everything on a device simply because it has been asked to complete a task.
Instead, its permissions should be limited, monitored and enforced by the operating system or the environment in which it runs.
Can AI Agents Work Without Sending Everything to the Cloud?
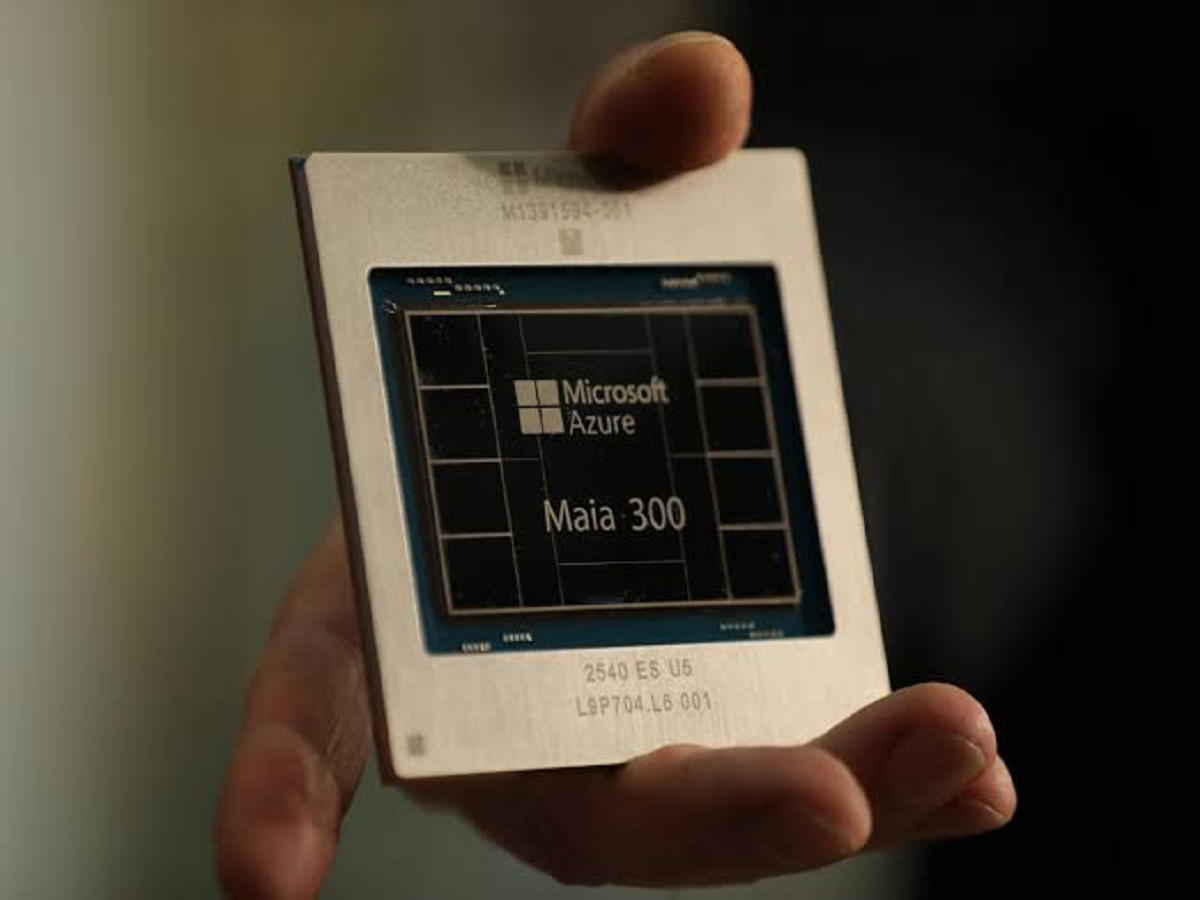
Another important development is the growing ability to run AI models directly on computers rather than relying entirely on remote data centres.
Local AI processing can offer potential privacy advantages because certain information can remain on the user's device. It may also reduce dependence on an internet connection for supported tasks.
However, local processing is not automatically secure. A model running on a computer can still access sensitive files or perform risky actions if it has excessive permissions. Strong access controls remain essential whether the AI operates locally or in the cloud.
Hardware requirements are another consideration. Powerful AI systems may require substantial memory and processing capacity, which can make capable local AI computers expensive.
What Should Ordinary Users Do to Stay Safe?
You do not need to avoid AI tools entirely to protect your information. Instead, use them carefully and understand what permissions they receive.
Here are five practical precautions:
-
Limit permissions: Give AI applications access only to the files, accounts and tools they genuinely need.
-
Review important actions: Require confirmation before an agent sends emails, deletes files, transfers money or changes important records.
-
Avoid sharing sensitive information unnecessarily: Do not upload passwords, banking details or confidential documents without understanding the service's data policies.
-
Keep software updated: Install operating-system and application security updates promptly.
-
Check connected applications: Periodically review which services your AI assistant can access and revoke permissions you no longer need.
Businesses should also maintain activity logs, test AI systems before deployment and establish clear procedures for investigating unexpected actions.
Will AI Agents Replace Traditional Software?
AI agents may change how people interact with software, shifting some tasks from manual navigation to natural-language instructions. Instead of opening several applications and completing each step independently, users may increasingly ask an assistant to coordinate the process.
However, conventional software will remain important for predictable operations, precise controls and tasks requiring strict accountability. AI agents are most useful when their capabilities are matched to the task and their actions can be verified.
The future is therefore unlikely to be about replacing every application with AI. It will be about combining intelligent assistance with reliable software controls.
The Future of AI Depends on Trust
AI agents could make computers more useful by automating repetitive work and helping people manage complicated tasks. But greater autonomy also means that mistakes can have wider consequences if systems are poorly designed or given excessive access.
The next stage of AI development will depend not only on how intelligent these tools become, but also on how effectively they protect information, respect permissions and keep users in control.
For consumers and businesses alike, the most important principle is simple: an AI agent should be powerful enough to help, but restricted enough to prevent it from doing things it was never authorised to do.